The arrest of a 41-year-old United States military service member near Gloucester has pushed the quiet machinery of counterintelligence into public view, and the details matter far more than the headline. British police detained the soldier under the National Security Act 2023, a statute deliberately drafted to modernise how the United Kingdom prosecutes espionage, foreign interference, and the disclosure of protected information. The allegations are said to relate to Russia, and searches were conducted at two locations in Gloucestershire. What elevates this case beyond a routine security incident is geography: the soldier was reportedly based at Imjin Barracks in Innsworth, the garrison that hosts NATO's Allied Rapid Reaction Corps, one of the alliance's most consequential operational headquarters.
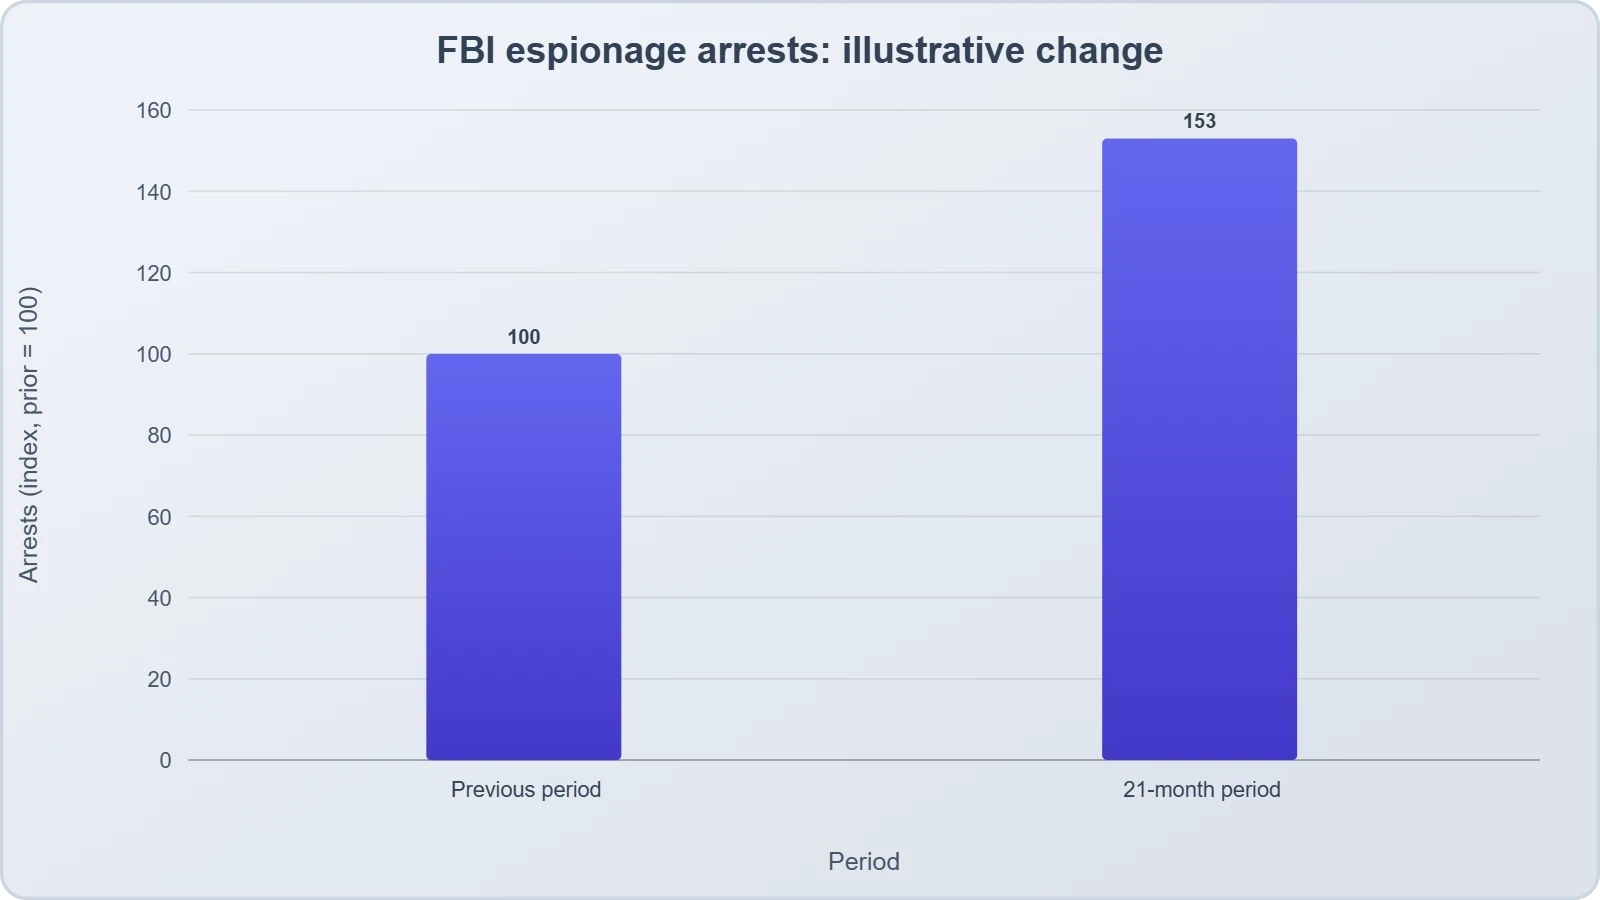
That single fact reframes the entire episode. Espionage cases usually involve diplomats, contractors, or civilian officials; a serving soldier allegedly compromising secrets from inside a NATO command hub touches the core of collective defence. The Metropolitan Police confirmed that Counter Terrorism Policing London is leading the investigation, that the man can be held without charge for up to 14 days, and that the inquiry is not connected to other counterterrorism operations. Deputy Assistant Commissioner Vicki Evans attributed the arrest to close UK-US cooperation, while FBI Director Kash Patel described the allegations as being of the utmost concern and disclosed 167 counterintelligence and espionage-related arrests over the past 21 months, a 53 percent rise over the comparable prior period.
Beyond the procedural facts, the case carries a doctrinal warning that military leaders rarely state so bluntly in public. Brigadier General Sean Stinchon, commanding general of US Army Counterintelligence Command, called the alleged conduct of a senior soldier entrusted with sensitive information a sobering reminder that insider threats are real and persistent. That framing is the analytical heart of the story: modern espionage is less about trench-coated handlers and more about trusted insiders with legitimate access, exploited through coercion, ideology, money, or grievance. This analysis examines the legal architecture, the NATO dimension, the insider threat doctrine, the transatlantic intelligence relationship, and the broader pattern of rising espionage allegations.
On This Page
- The Legal Architecture of the National Security Act 2023
- Imjin Barracks and the NATO Dimension
- Insider Threats and the Psychology of Betrayal
- The Transatlantic Intelligence Relationship Under Strain
- The Rising Tide of Espionage Arrests
- Institutional Consequences and the Road Ahead
- Frequently Asked Questions
TL;DR A 41-year-old US soldier was arrested near Gloucester, England, on suspicion of espionage linked to Russia, detained under the National Security Act 2023 after an investigation led by Counter Terrorism Policing London. The soldier was reportedly based at Imjin Barracks in Innsworth, home to NATO's Allied Rapid Reaction Corps, making the case a rare alleged insider compromise at the heart of alliance infrastructure. Police can hold him without charge for up to 14 days, and searches continue at two Gloucestershire locations. FBI Director Kash Patel cited 167 counterintelligence arrests in 21 months, a 53 percent increase, while US Army counterintelligence officials described insider threats as real and persistent. It is believed to be the first case of a US soldier suspected of spying for a foreign government while stationed in the UK.
The Legal Architecture of the National Security Act 2023
The National Security Act 2023 replaced a patchwork of antiquated espionage statutes, some of which dated back to the Official Secrets Acts of 1911 and 1920, and consolidated them into a single modern framework designed for a world of state-backed cyber operations, foreign interference, and proxy espionage. The Act created offences that did not previously exist in clear form, including foreign interference, sabotage, and assisting a foreign intelligence service. Crucially, it also extended jurisdiction extraterritorially, meaning conduct abroad by British nationals or others with a close connection to the UK can be prosecuted domestically. For prosecutors, the statute offers sharper tools; for defence lawyers, it raises complex questions about intent, protected information, and the boundaries of legitimate security work.
Two sections of the Act are central to this case. Section 1 criminalises obtaining, copying, recording, or disclosing protected information where the conduct is intended to benefit a foreign power or is otherwise prejudicial to the safety or interests of the United Kingdom. Section 3 addresses assisting a foreign intelligence service, which can encompass a far broader range of conduct than the classic passing of documents, including providing material support, introductions, or logistical help. The distinction matters because Section 1 focuses on the information itself, while Section 3 focuses on the relationship with the foreign service. Police have not specified which provision forms the basis of suspicion, and under British practice suspects are generally not named before charge.
Detention Powers and the Fourteen-Day Window
The power to hold a suspect without charge for up to 14 days is one of the most significant features of the Act, and it is deliberately exceptional. Pre-charge detention of this length exists because espionage investigations often involve encrypted devices, classified material requiring damage assessment, and coordination with allied services that cannot be rushed. The clock is not unlimited, however; extensions require judicial authorisation, and the suspect retains rights to legal representation. In practice, the 14-day window signals to investigators that they are dealing with material whose sensitivity demands careful forensic handling rather than a rapid charging decision.
That extended window also shapes the public narrative. Because police rarely name suspects before charge, and because much of the evidence will be classified, the case may remain opaque for months. Observers should therefore treat early reporting with appropriate caution: the arrest is a suspicion, not a conviction, and the legal process must run its course. The involvement of counterterrorism policing reflects organisational structure rather than the nature of the alleged offence, since Counter Terrorism Policing London holds national responsibility for espionage and state-threat investigations in England and Wales.
Why the Statute Matters Beyond This Case
The Act represents a strategic shift in how liberal democracies legislate against hostile state activity. Rather than waiting for a completed act of betrayal, the framework allows earlier intervention against conduct that creates risk, such as reconnaissance of sensitive sites or cultivation of sources. Civil liberties groups have raised concerns about breadth and vagueness, particularly around the foreign interference provisions, while security officials argue the thresholds contain adequate safeguards. The balance struck here will be tested in court, and the outcome will shape how aggressively the UK pursues state-linked threats in the coming decade.
For allied governments watching, the case is also a template. Canada, Australia, and the United States have all modernised their espionage laws in recent years, and the UK statute is among the most comprehensive. Its use against a serving allied soldier, rather than a British national, will test how the Act interacts with status-of-forces arrangements and military justice. Those legal interfaces are rarely examined in public, yet they determine whether a case proceeds in civilian courts, military courts, or both.
Imjin Barracks and the NATO Dimension
Imjin Barracks at Innsworth is not an ordinary garrison. Since 2010 it has housed the headquarters of NATO's Allied Rapid Reaction Corps, a multinational formation designed to deploy quickly in crisis and to provide command capacity for the alliance's most demanding operations. The ARRC has led missions in the Balkans and Afghanistan and remains a linchpin of NATO's command structure. A security breach at such a site is therefore not merely a British domestic matter; it implicates the collective defence architecture that binds thirty-plus nations. That is why the language used by US officials was unusually direct and why the case has drawn attention far beyond Gloucestershire.
The presence of a US soldier at a NATO headquarters is routine, reflecting the deep integration of allied forces. But that integration creates a distinctive vulnerability: multinational sites concentrate sensitive information from many nations in one place, and access is granted to personnel from many countries. The insider threat at such facilities is not hypothetical; it is a structural feature of coalition warfare. Counterintelligence services must therefore vet not only their own nationals but also monitor the behaviour of allied personnel, a task that requires trust and information-sharing at a level few institutions can sustain.
Why Coalition Hubs Attract Intelligence Services
Foreign intelligence services prize coalition headquarters because a single well-placed source can yield insight into multiple nations' planning, capabilities, and intentions. Russia has long demonstrated interest in NATO's command arrangements, force generation, and political-military decision-making. A source inside a headquarters can reveal not only operational plans but also the alliance's assumptions, its readiness gaps, and the political constraints on member states. That intelligence is often more valuable than any single document, because it shapes strategic assessment rather than tactical action.
The concentration effect also means damage assessment is complicated. When information is compromised at a multinational hub, investigators must determine which nations' secrets were exposed, which requires coordinated notification and remediation across capitals. That process is slow, classified, and rarely visible. The public may never learn the full extent of what was allegedly accessed, which is precisely why officials speak in terms of seriousness rather than specifics.
The Status-of-Forces Question
Cases involving allied service members raise intricate questions under status-of-forces agreements, which govern how sending states and host states share criminal jurisdiction over military personnel. Generally, the sending state retains primary jurisdiction over offences committed by its personnel in the performance of duty, while the host state may exercise jurisdiction in other circumstances. Espionage allegations complicate that calculus because they implicate host-state national security directly. The resolution will depend on diplomatic negotiation as much as legal doctrine, and the outcome may set a precedent for future cases.
For the United States, the case also tests the credibility of its own counterintelligence messaging. American officials have spent years warning allies about insider threats and the persistence of Russian intelligence activity. When one of its own soldiers is accused, the response must demonstrate that the warnings apply internally as well as externally. The FBI's public statements, including the arrest statistics, appear designed to signal exactly that: the machinery is working, and no one is exempt.
Insider Threats and the Psychology of Betrayal
Insider threats are the hardest category of security risk to manage because they exploit legitimate access rather than breaching defences. A soldier with clearance does not need to hack a system; he or she simply walks through the door. Counterintelligence doctrine therefore focuses on behaviour, motive, and opportunity rather than perimeter security. The classic drivers are money, ideology, coercion, and ego, often summarised in intelligence literature as the MICE framework, though modern practice recognises more complex combinations including grievance, addiction, and personal crisis. Detection depends on colleagues noticing changes and reporting them.
Brigadier General Stinchon's remark that insider threats are real and persistent reflects a hard-earned institutional lesson. Repeated espionage cases across Western militaries have shown that no vetting regime is perfect and that trusted insiders can operate for years before detection. The emphasis on reporting suspicious behaviour is not bureaucratic boilerplate; it is the primary detection mechanism available. Yet reporting cultures vary, and fear of damaging a colleague's career can suppress exactly the observations that matter most.
Detection, Vetting, and Continuous Evaluation
Modern security clearance regimes have moved from periodic reinvestigation toward continuous evaluation, using automated checks of financial records, travel, and legal databases to flag risk indicators in near real time. The logic is that betrayal rarely begins abruptly; it develops through observable stressors. Continuous evaluation aims to catch those signals earlier. Critics worry about privacy and false positives, while practitioners argue the alternative, episodic review every five or ten years, leaves dangerous gaps during which a person's circumstances can change dramatically.
Vetting alone cannot solve the problem, however. The most damaging cases often involve individuals who passed every check and whose motives were internal and invisible. Human intelligence officers exploit precisely those inner vulnerabilities, offering validation, purpose, or rescue from financial ruin. Countering that requires more than forms and interviews; it requires a culture in which people feel able to disclose pressure before it becomes leverage.
The Reporting Imperative
The instruction to report suspicious activity is easy to state and difficult to operationalise. Effective programmes reduce the social cost of reporting, protect confidentiality, and ensure that reports lead to proportionate inquiry rather than overreaction. When reporting channels are trusted, they generate useful signal; when they are feared, they generate silence. The Gloucester case will likely prompt renewed emphasis on these mechanisms across NATO formations, particularly among multinational staff who may be unsure which national authority to approach.
There is also a leadership dimension. Senior soldiers entrusted with sensitive information are expected to model security consciousness, which is why the phrase "senior soldier" in official statements carries weight. When someone at that level is accused, the institutional response must address both the specific allegation and the broader question of whether security culture at the unit level was adequate. That inquiry will unfold largely out of public view.
We Also Published
The Transatlantic Intelligence Relationship Under Strain
The UK-US intelligence relationship is the deepest bilateral partnership in the world, anchored in the Five Eyes arrangement alongside Australia, Canada, and New Zealand. It rests on shared classification standards, reciprocal access, and decades of operational trust. A case in which an American soldier is accused of betraying secrets on British soil tests that relationship in a specific way: it requires British investigators to examine US personnel while US agencies cooperate in the inquiry. Both governments have emphasised partnership, but the operational friction is real and must be managed carefully.
Deputy Assistant Commissioner Evans framed the arrest as evidence of the strength of UK-US law enforcement and national security partnerships, a diplomatic formulation that also serves a practical purpose. Public confidence in the alliance depends on visible cooperation, particularly when the alleged conduct involves a trusted insider. The FBI's decision to comment publicly, including specific arrest statistics, reinforces that message. Silence would have invited speculation about friction; transparency, carefully bounded, projects competence.
Five Eyes and the Trust Premium
Five Eyes members share intelligence on the understanding that handling standards are equivalent and that personnel are vetted to comparable thresholds. When an insider compromise occurs, the affected partners must assess whether the breach originated in a systemic weakness or an individual failure. That assessment determines whether access arrangements need adjustment. Historically, the alliance has absorbed individual betrayals without structural rupture, but each case consumes trust that must be rebuilt through audits, briefings, and demonstrated remediation.
The trust premium also explains why espionage allegations are treated with such gravity even before charges are filed. The damage is not only to the information allegedly compromised but to the confidence that partners place in each other's personnel systems. Rebuilding that confidence requires evidence that the problem was detected, investigated, and corrected. The speed and transparency of the current inquiry will therefore matter as much as its eventual legal outcome.
Political Context and the Russia Factor
The allegations arise against a backdrop of sustained tension with Russia, including the ongoing war in Ukraine and repeated warnings from Western intelligence agencies about Russian sabotage, assassination plots, and recruitment operations across Europe. In that environment, espionage cases are interpreted as part of a broader campaign rather than isolated incidents. Officials are careful not to prejudge guilt, but the political framing is unmistakable: hostile state activity is persistent, and allies must respond collectively.
That framing carries risks as well as benefits. Overstating the threat can inflate public anxiety and complicate due process, while understating it can leave vulnerabilities unaddressed. The mature approach, which British and American officials appear to be following, is to describe the seriousness of the allegations while emphasising that the legal process will determine guilt. That balance protects both national security and the presumption of innocence.
The Rising Tide of Espionage Arrests
The FBI's disclosure of 167 counterintelligence and espionage-related arrests over 21 months, a 53 percent increase over the comparable previous period, is the most concrete data point in the entire episode. It suggests that detection has improved, that hostile activity has intensified, or, most likely, both. Arrest statistics are an imperfect measure because they reflect enforcement priorities and reporting practices as much as underlying threat levels. Nevertheless, a jump of that magnitude across a defined period is difficult to attribute to statistical noise alone.
Several factors plausibly contribute. Western services have invested heavily in counterintelligence since 2022, expanding teams and improving coordination with allies. Russia's intelligence apparatus has been forced to rely more on human sources as diplomatic cover shrinks and cyber operations face stronger defences. Meanwhile, insider threat programmes have matured, generating more referrals. The result is a higher tempo of investigations reaching the arrest stage, even as the most sophisticated operations likely remain undetected.
Reading the Numbers Carefully
Arrest figures should be interpreted with caution. A rise in arrests may indicate success in detection rather than an increase in offending, and different agencies count cases differently. Some arrests involve attempted recruitment, others involve actual transmission of secrets, and others involve export control or sanctions violations bundled into counterintelligence portfolios. Without disaggregated data, the headline percentage is best understood as a directional signal rather than a precise measurement of threat.
What the numbers do establish is institutional attention. Senior officials are willing to publicise enforcement activity, which signals political priority and resource commitment. That publicity serves deterrence, warning potential recruits that detection is likely. It also serves reassurance, demonstrating that governments are responding to a threat their publics increasingly perceive. Both functions depend on the figures being credible, which is why agencies tend to publish them sparingly and with context.
Comparative Enforcement Patterns
Across Europe, espionage and sabotage cases have multiplied since 2022, with arrests in Germany, Poland, the Baltic states, and elsewhere linked to Russian intelligence. The pattern is consistent: recruitment of marginal figures, use of proxies, and targeting of logistics, military assistance, and critical infrastructure. The Gloucester case differs in the seniority of the alleged insider and the sensitivity of the location, but it fits the broader trend of intensified hostile activity against NATO members and partners.
Comparative analysis also reveals variation in legal responses. Some states rely on criminal espionage statutes, others on national security laws, and others on immigration or terrorism provisions. The UK's National Security Act is among the most modern, and its use in this case will provide a test of how effectively contemporary legislation handles complex, multinational investigations. Other capitals will be watching closely.
Institutional Consequences and the Road Ahead
The immediate consequences will unfold quietly: damage assessments, briefings to allies, reviews of access controls at Imjin Barracks, and interviews with colleagues. The public will see little of this work, which is appropriate given classification requirements. What can be observed is the tone of official statements, and that tone has been notably coordinated. British and American officials have emphasised partnership, seriousness, and the persistence of insider threats, a triad designed to reassure allies while warning potential offenders.
Longer term, the case may accelerate reforms already underway. Continuous evaluation, insider threat reporting platforms, and multinational security protocols are all likely to receive renewed attention. The ARRC's multinational character makes it a natural pilot site for improved vetting coordination among allies. If the case reveals gaps in how coalition personnel are monitored, those gaps will need closing without eroding the interoperability that makes the headquarters effective.
Accountability and Due Process
It bears repeating that an arrest is not a conviction. The suspect has not been charged, and under British law he benefits from the presumption of innocence and the right to a fair trial. The seriousness of the allegations does not suspend those protections; indeed, the more serious the charge, the more important the procedural safeguards become. Public commentary should reflect that balance, resisting the temptation to treat suspicion as proof.
The legal process will also determine what the public learns. If the case proceeds to trial, sensitive material may be heard in closed session or replaced by summaries to protect sources and methods. That opacity is frustrating for observers but necessary for security. The eventual verdict, whatever it is, will be only the visible tip of an investigative effort that spans two countries and multiple agencies.
What This Case Signals About the Threat Environment
The most durable lesson is that espionage has returned to the centre of Western security planning. The post-Cold War assumption that state espionage had become a marginal activity has been thoroughly overturned. Russia's intelligence services remain active, motivated, and willing to recruit from within allied militaries. Other state actors pose comparable risks. Institutions that treat counterintelligence as a legacy function do so at their peril; the Gloucester case demonstrates that the threat is operational, current, and close to home.
For readers following security affairs, the case offers a useful case study in how modern democracies respond: through legislation designed for the threat, through multinational cooperation, through public messaging calibrated to reassure and deter, and through legal processes that must balance security against liberty. The details will emerge slowly, but the framework is already visible, and it will shape how similar cases are handled for years to come.
Frequently Asked Questions
Readers encountering this story through headlines often have the same set of practical questions: who was arrested, under what law, why the case matters, and what happens next. The answers are partly factual and partly analytical, because the significance of the case lies in what it reveals about the security environment rather than in the bare details of the detention. The following questions address the most common points of confusion, separating what is known from what remains speculative and explaining the legal and institutional context that gives the episode its weight.
What Is Known and What Remains Unclear
Confirmed facts include the arrest of a 41-year-old US military member near Gloucester, detention under the National Security Act 2023, searches at two locations, and the involvement of Counter Terrorism Policing London. The allegations relate to Russia. Unclear elements include the specific conduct alleged, which statutory provision forms the basis of suspicion, the soldier's exact role and clearance level, and whether charges will follow. Speculation about the nature of the alleged betrayal should be treated cautiously until official information emerges.
It is also unclear how the case will interact with military justice. The US military has its own investigative and disciplinary systems, and parallel proceedings are possible. Coordination between British civilian authorities and American military counterparts will determine the forum. Historically, such cases are resolved through diplomatic and legal negotiation, and the outcome may not be publicly detailed. Readers should expect incremental disclosure rather than a single comprehensive account.
Why the Location Matters So Much
Imjin Barracks hosts NATO's Allied Rapid Reaction Corps, a headquarters with multinational staff and significant operational planning responsibilities. A security incident there implicates not only British and American interests but those of every alliance member. That is why the case has drawn attention from senior officials in both countries and why the language used has been unusually direct. The location transforms a routine espionage allegation into a test of coalition security arrangements.
The barracks' role also explains the emphasis on insider threats. Multinational headquarters concentrate sensitive information and grant access to personnel from many nations, creating structural vulnerabilities that cannot be eliminated by perimeter security alone. Counterintelligence at such sites depends on vetting, behavioural monitoring, and trust among allies. When that trust is tested, the institutional response must demonstrate that the system detected the problem and can correct it.
From our network :
- Live Online English Classes for Kids: Do They Actually Reduce Anxiety?A ten-week study reveals that synchronous online English classes can significantly reduce child language anxiety while improving listening and reading skills. Discover what makes these programs effective and how parents can select the right one.
- Mobile Learning and VR in English: What Global Evidence Reveals About Effective Language TechnologyA systematic review across 14 countries reveals which language-learning technologies genuinely work. Mobile learning, AI, and VR show measurable benefits when pedagogically integrated. This evidence-based guide helps educators and learners select technology that delivers real return on investment.
- Committed Mediterranean Precipitation Decline: Why Emissions Cuts Alone Cannot Restore Winter RainsNew NOAA research reveals that Mediterranean winter rains may decline irreversibly even with emissions cuts. Explore the science of committed climate change and regional impacts.
- University Language Proficiency Exams: Why Institutional Tests Demand Different Preparation Than IELTS and TOEFLDiscover why university-specific language proficiency examinations differ fundamentally from IELTS and TOEFL, and learn strategic preparation approaches for institutional assessment success.
- CISA’s Ten-Advisory Wave: Why Generic Patching Fails in OT and How to Build Product-Specific PlaybooksCISA released ten ICS advisories in one week, exposing critical infrastructure risks. Generic patching fails in OT. Learn to build product-specific remediation playbooks.
- The Hidden Cost of AI Convenience: Why Over-Permissioned Agents Are a Security Time BombDiscover why AI agents with excessive permissions create dangerous single points of failure, and learn how implementing least privilege principles can protect your organization from exploitation.
- The Final Descent: How ESA Retired the Legendary Cluster Constellation After 24 Years of Space Weather ScienceAfter 24 years mapping Earth’s magnetosphere, ESA’s Cluster mission concluded with a precisely controlled reentry over the South Pacific. This analysis explores the scientific legacy, engineering decisions, and debris mitigation principles behind one of space exploration’s most responsible retirements.
- Forbidden Matrix Patterns and Visible Lattice Points: A Geometric DictionaryExplore how multidimensional 0–1 matrices encode geometric truths, linking forbidden patterns to visible lattice points and hypergraph theory, with applications in combinatorics and computational geometry.
- How AI Agents Will Change the Way We Manage Personal FinancesExplore how AI agents are transforming personal finance through automated budgeting, bill payment, and investment management, while examining the critical security protocols and governance frameworks required for safe deployment.
RESOURCES
- US Army soldier suspected of spying for Russia arrested in UK - BBCbbc.com20 hours ago ... Counter Terrorism Policing London said the man had been arrested under section one and section three of the National Security…
- U.S. soldier arrested in Britain accused of espionage linked to Russiapbs.org21 hours ago ... The 41-year-old man, who was not named, was arrested near Gloucester on suspicion of violating two sections of the National…
- US soldier accused of spying for Russia arrested in the UK: Officialsabc7ny.com4 hours ago ... The soldier was arrested on suspicion of violating offenses under the U.K.'s National Security Act of 2023, which is a…
- US Army member arrested in UK for suspected 'espionage' for Russiareuters.com20 hours ago ... The US Army soldier arrested on Tuesday was detained on suspicion of offences under sections 1 and 3 of the…
- American soldier arrested on suspicion of spying for Russia - CNBCcnbc.com8 hours ago ... The 41-year-old man is being detained in London under the U.K.'s National Security Act.
- Senior U.S. Army soldier arrested in U.K. on suspicion of assisting ...nbcnews.com18 hours ago ... U.S. soldier charged with spying for Russia ... He was arrested on suspicion of offenses under sections 1 and 3…
- US soldier arrested for Russia spying: What we know - Al Jazeeraaljazeera.com4 hours ago ... A 41-year-old man has been arrested near Gloucester on suspicion of offences under the National Security Act ... Britain's National…
- US Soldier Is Arrested in UK on Suspicion of Spying for Russianytimes.com18 hours ago ... ... detained on suspicion of violating Section 1 and Section 3 of Britain's National Security Act 2023. Those sections relate…
- US Army soldier arrested in UK on suspicion of espionage related to ...cnn.com21 hours ago ... A 41-year-old United States Army soldier was arrested in the United Kingdom on Tuesday on suspicion of espionage related to…
- US Army soldier suspected of spying for Russia arrested in UK - BBCbbc.co.uk21 hours ago ... Counter Terrorism Policing London said the man had been arrested under section one and section three of the National Security…
- Member of U.S. Army arrested as part of UK Counter Terrorism ...army.mil18 hours ago ... He was arrested on suspicion of offences under Section 1 and Section 3 of the National Security Act 2023. As…
- U.S. soldier accused of spying linked to Russia arrested in the U.K.cbsnews.com18 hours ago ... The soldier is suspected of violations under Section 1 and Section 3 of the U.K.'s National Security Act of 2023…
- A 41-year-old United States Army soldier was arrested in ... - Facebookfacebook.com18 hours ago ... ... charged under the National Security Act 2023, according to The Guardian. ... 3 people arrested on suspicion of spying…
- US soldier accused of spying for Russia arrested in the UK: Officialsabcnews.com18 hours ago ... The soldier was arrested on suspicion of violating offenses under the U.K.'s National Security Act of 2023, which is a…
- A member of the U.S. Army was arrested Tuesday in England on ...facebook.com19 hours ago ... U.S. soldier arrested in Britain accused of espionage linked to Russia ... National Security Act 2023. The post notes that…
- 01
- 02
- 03
- 04
- 05
- 06
- 07
- 08
0 Comments