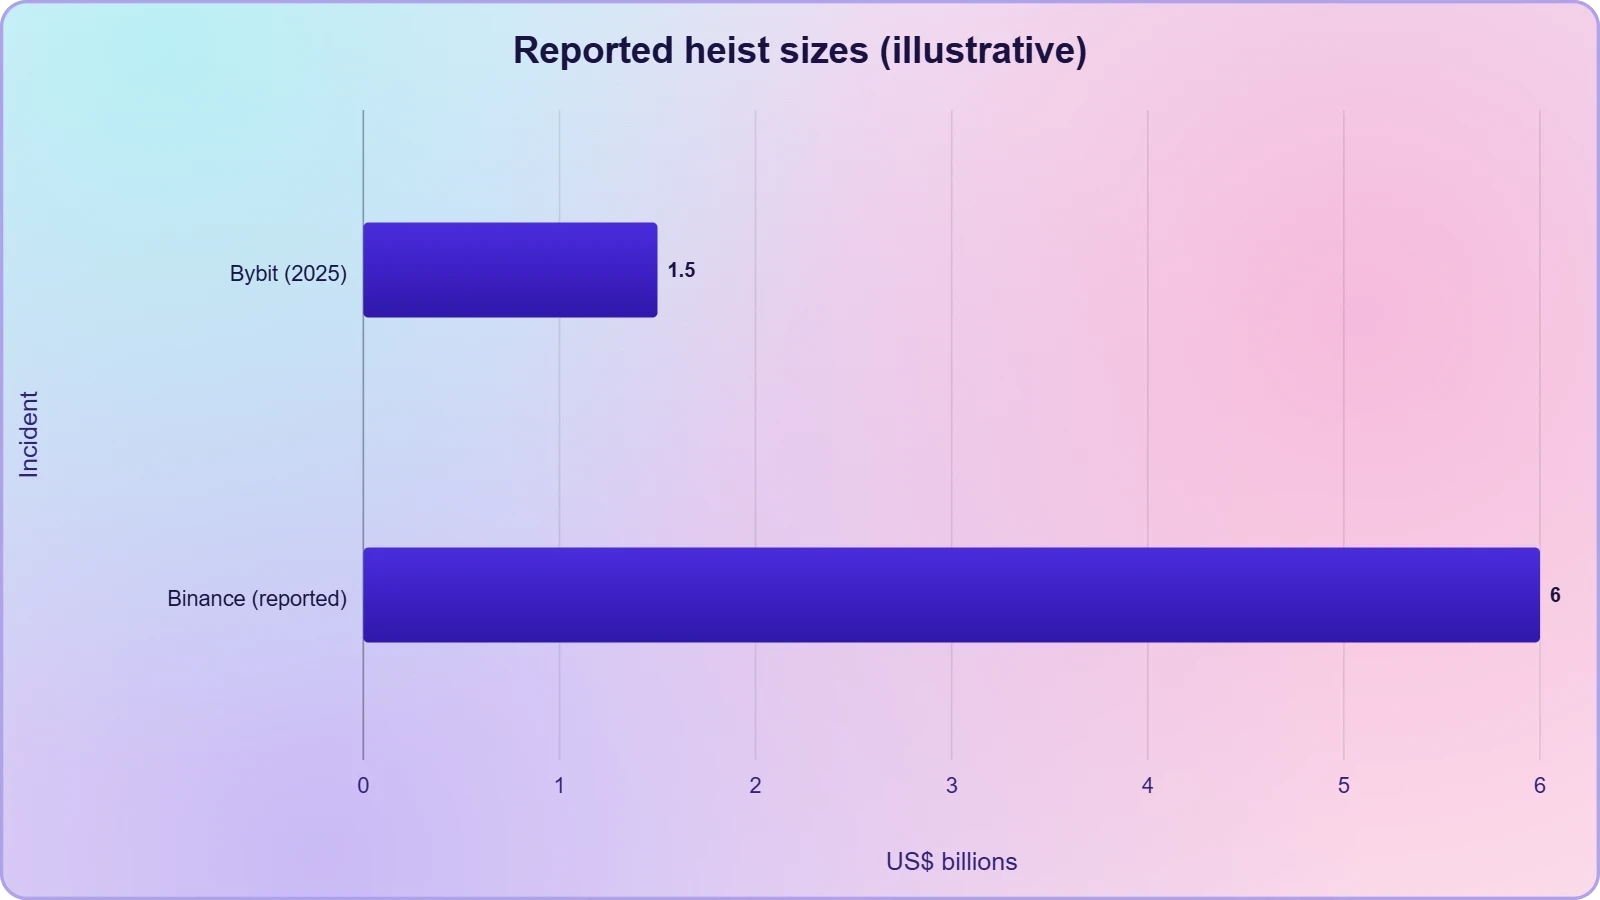
The reported theft of more than $6 billion from Binance has instantly become the largest cryptocurrency exchange heist ever documented, dwarfing the roughly $1.5 billion Bybit raid of 2025 that investigators also pinned on Pyongyang-linked operators.
At the centre of the dispute sits a blunt diplomatic confrontation: Washington's FBI attributes the breach to a state-tied group tracked as TraderTraitor, while North Korea's leadership dismisses the charge as fabrication.
Kim Yo Jong, speaking through the state news agency KCNA, framed the allegation as a serious political provocation and insisted it carries nothing new.
On This Page
What elevates this episode beyond a routine security post-mortem is the speed and scale involved. Blockchain analytics firm TRM Labs tied the attack to the same cluster of actors and reported that most of the funds were moved out within twenty minutes, a velocity that speaks to rehearsed infrastructure rather than opportunistic crime.
Binance, for its part, confirmed it had replaced most of the stolen assets using its own balance sheet and outlined a staged resumption of withdrawals across several chains. The exchange's response and Pyongyang's denial now form two competing narratives over the same forensic trail.
The implications stretch well past one exchange's treasury. Analysts in Seoul read the unusually swift denial as a signal that North Korea fears tighter financial containment of a revenue stream widely believed to underwrite its weapons programmes.
Every attribution of this kind therefore becomes a geopolitical instrument as much as a technical finding, shaping sanctions debates, exchange compliance budgets and the willingness of summit diplomacy to restart. The sections below examine the heist's mechanics, the attribution dispute, the exchange's recovery playbook and the wider consequences for digital-asset security.
TL;DR North Korea has rejected FBI accusations that its TraderTraitor hacking group stole more than $6 billion from Binance, with Kim Yo Jong calling the charge a political provocation. TRM Labs linked the breach to the same actors and noted most funds moved within twenty minutes. Binance says it replaced most stolen assets from its own funds and is restoring withdrawals across multiple blockchains. The dispute matters because attribution now drives sanctions, exchange security spending and stalled diplomacy.
The Anatomy of a Record-Breaking Exchange Breach
The Binance incident belongs to a distinct category of crypto crime: the state-adjacent exchange heist, where intrusion, laundering and diplomatic denial operate as one continuous process. Unlike ransomware crews that negotiate with victims, these operators treat exchange hot wallets as strategic revenue targets and move with industrial discipline.
The reported figure of more than $6 billion places the event in a league of its own, roughly quadrupling the Bybit loss recorded a year earlier.
How the Funds Moved So Quickly
TRM Labs' finding that most of the money left within twenty minutes is the most operationally revealing detail in the entire episode. Such velocity implies pre-positioned wallets, automated splitting scripts and laundering routes tested in advance, not improvised transfers.
Investigators typically trace these flows through chain-hopping, mixers and over-the-counter desks that convert tokens into fiat or stablecoins.
Speed also complicates recovery. Once assets disperse across hundreds of addresses and multiple chains, exchanges and analytics firms must coordinate freeze requests in minutes rather than days. The window for intervention effectively closes before conventional incident response even begins, which is precisely why the twenty-minute figure has unsettled security teams across the industry.
The TraderTraitor Playbook
TraderTraitor, the designation used by US authorities, describes a cluster of activity rather than a single malware family. Public reporting has long associated the label with social-engineering campaigns targeting developers and crypto employees through fake job offers, trojanised software repositories and credential theft. The pattern favours patience and human manipulation over brute-force exploitation of smart contracts.
That approach explains why exchange perimeter defences alone rarely suffice. A single compromised engineer credential can bypass layers of infrastructure hardening, granting access to signing systems and treasury workflows. Defenders must therefore treat personnel as part of the attack surface, pairing technical controls with verification protocols for recruitment outreach and third-party tooling.
The Attribution Dispute and Pyongyang's Denial
Attribution in cybercrime is never a purely technical exercise, and this case demonstrates why. The FBI's public statement named TraderTraitor and effectively accused a sovereign state of orchestrating commercial theft on an unprecedented scale.
Pyongyang's response arrived with equal speed, framing the claim as a hostile political act rather than a forensic conclusion, and signalling that the dispute will be fought in diplomatic channels as much as on-chain.
Kim Yo Jong's Framing of the Accusation
Kim Yo Jong's statement, carried by KCNA, described the US allegation as absurd and nothing new, positioning North Korea as the habitual target of Washington's hostility. She suggested Pyongyang now has issues to reconsider in light of the charge.
That language matters because it links a criminal accusation to the broader question of whether summit talks can resume.
By treating the FBI finding as provocation rather than evidence, the statement reframes the debate from blockchain forensics to sovereign grievance. It also implicitly acknowledges that the accusation carries material consequences, since attribution of this kind typically triggers sanctions designations, asset freezes and pressure on exchanges to tighten monitoring of North Korean-linked wallets.
Why Seoul Analysts Read Speed as Anxiety
Analysts quoted by Reuters in Seoul interpreted the rapid denial as a tell. A regime confident in its insulation from financial pressure might ignore the charge entirely; a swift rebuttal suggests concern that Washington could escalate efforts to sever a funding stream believed to finance weapons development. The denial thus functions as defensive diplomacy.
That reading aligns with the broader pattern of North Korean crypto activity, which Western governments have long characterised as a revenue channel for missile and nuclear programmes. Each successful heist strengthens the case for tighter enforcement, making every attribution a potential turning point in the financial containment campaign.
Binance's Recovery Playbook and Withdrawal Restoration
Binance's public response has focused on continuity rather than confrontation. The exchange confirmed it replaced most of the stolen assets using its own funds, a decision that shields users from immediate loss but raises questions about reserve adequacy and disclosure standards.
It then announced a phased restoration of withdrawals, beginning at 04:00 GMT on Tuesday across several major networks.
The Chains Coming Back Online
The rollout covers Binance Smart Chain, Ethereum, Solana, XRP and Sui, with selected tokens on Arbitrum, Optimism, Tron and Base included in the same schedule. Staging the restart by chain rather than switching everything on at once is a deliberate risk-control choice, allowing engineers to verify balances and liquidity chain by chain.
For users, the practical question is whether restored access reflects genuine solvency or temporary accommodation. Exchanges that self-fund reimbursements must draw on retained earnings, insurance reserves or token holdings, and each option carries trade-offs that markets eventually price. Transparency about the source of replacement funds would materially strengthen confidence.
What Self-Funding Signals to Markets
Absorbing a multi-billion-dollar loss without passing it to customers is a powerful reputational statement, but it also concentrates risk. If reserves are depleted, the exchange's buffer against future incidents narrows, and counterparties may demand stronger proof of solvency. The market's reaction over coming weeks will reveal how credible the reimbursement is judged to be.
Regulators are likely to treat the episode as a case study in custody risk. Expect renewed scrutiny of proof-of-reserves practices, segregation of customer assets and the adequacy of insurance arrangements, particularly for platforms holding systemic volumes of retail and institutional capital.
- 01
- 02
- 03
- 04
Geopolitical Fallout and the Sanctions Question
Beyond the balance sheet lies a familiar geopolitical equation. Western governments have spent years arguing that North Korean crypto theft underwrites prohibited weapons programmes, and each large heist strengthens that case in policy debates.
Attribution therefore becomes leverage, giving Washington grounds to press allies, exchanges and analytics providers toward stricter enforcement of wallet blacklists and travel-rule compliance.
Funding Weapons Through Digital Assets
The scale of the reported loss matters because it converts an abstract threat into a quantifiable revenue estimate. If a single operation can net billions, the incentive structure for state-linked groups is overwhelming, and defensive spending by exchanges must scale accordingly. Sanctions designations typically follow, targeting wallets and intermediaries rather than the state directly.
Enforcement, however, depends on cooperation from jurisdictions where laundering infrastructure resides. Chain-hopping and over-the-counter conversion frequently route through lightly regulated venues, meaning the effectiveness of any response hinges on international coordination that has historically been uneven and slow to materialise.
Diplomacy Stalled and the Summit Question
North Korea has so far not responded to proposals to restart summit talks, and the Binance dispute adds another obstacle to any thaw. Pyongyang's framing of the accusation as provocation suggests it will treat the charge as evidence of US hostility rather than a matter for negotiation, hardening its public posture ahead of any future contact.
For Washington, the episode reinforces the argument that engagement without financial pressure is naive. For Seoul, it sharpens a strategic dilemma: pursuing dialogue while relying on the same attribution findings that Pyongyang rejects as political theatre. Neither side has an obvious incentive to soften its position soon.
Lessons for Exchange Security and Digital-Asset Custody
The episode offers an uncomfortable lesson for an industry that has spent a decade promising institutional-grade custody. A breach of this magnitude, executed with such speed, suggests that defensive investment has lagged behind adversary capability.
Exchanges now face pressure to demonstrate that treasury architecture, key management and personnel vetting meet standards comparable to systemically important financial institutions.
Hardening the Human Layer
Because TraderTraitor-style operations rely on social engineering, technical controls alone cannot close the gap. Recruitment-themed phishing, fake developer tools and credential harvesting target individuals rather than protocols. Firms must therefore institutionalise verification, limit privileged access and rehearse incident response for scenarios in which an insider credential is already compromised.
Practical measures include hardware-backed key custody, multi-party approval for large transfers, out-of-band verification for vendor communications and continuous monitoring of developer environments. None is novel, yet the persistence of successful intrusions suggests adoption remains inconsistent across even the largest platforms.
Rebuilding User Trust After a Heist
Trust, once damaged, is expensive to restore. Binance's decision to cover most losses from its own funds buys goodwill, but durable confidence requires verifiable proof that customer assets are segregated and reserves are sufficient. Independent attestations, published regularly, would do more than any single statement of reassurance.
Users, meanwhile, face a familiar calculus: convenience against counterparty risk. The rational response is diversification across custodial and self-custodial arrangements, combined with vigilance about withdrawal delays and reserve disclosures. The heist is a reminder that exchange balances are claims, not possessions.
Reading the Signal in a Contested Attribution
What ultimately distinguishes this episode is not the dollar figure but the contest over meaning. A forensic finding, a diplomatic denial and a corporate recovery plan are being advanced simultaneously, each competing to define what actually happened.
Observers should treat every claim as provisional until independent verification emerges, because attribution in state-linked cybercrime is inherently adversarial.
What to Watch in the Coming Weeks
Several indicators will clarify the picture. On-chain analysts will track whether stolen funds continue moving through mixers or settle into identifiable exchange deposits. Binance's withdrawal restoration will reveal whether liquidity holds under stress. And Washington's next sanctions tranche will show whether the accusation translates into enforceable measures rather than rhetoric.
Diplomatic signals matter equally. Any softening in Pyongyang's language, or renewed interest in talks, would suggest the financial pressure argument carries weight. Conversely, continued silence would indicate that the regime calculates the cost of engagement exceeds the cost of isolation.
Why Attribution Itself Is the Battleground
Attribution shapes insurance claims, regulatory findings and public confidence, which is why states contest it so vigorously. A denial need not be credible to be useful; it buys time, muddies enforcement and complicates the evidentiary record.
The Binance case will likely be cited for years as an example of how technical evidence and political narrative collide.
For the industry, the practical takeaway is that security is now a geopolitical function. Exchanges operating at systemic scale must plan for adversaries with state resources, patience and a willingness to absorb public denial. Preparedness, transparency and speed of response will determine who retains trust when the next record heist occurs.
Also Read
From our network :
- The Hidden Cost of AI Convenience: Why Over-Permissioned Agents Are a Security Time BombDiscover why AI agents with excessive permissions create dangerous single points of failure, and learn how implementing least privilege principles can protect your organization from exploitation.
- Live Online English Classes for Kids: Do They Actually Reduce Anxiety?A ten-week study reveals that synchronous online English classes can significantly reduce child language anxiety while improving listening and reading skills. Discover what makes these programs effective and how parents can select the right one.
- Committed Mediterranean Precipitation Decline: Why Emissions Cuts Alone Cannot Restore Winter RainsNew NOAA research reveals that Mediterranean winter rains may decline irreversibly even with emissions cuts. Explore the science of committed climate change and regional impacts.
- The Final Descent: How ESA Retired the Legendary Cluster Constellation After 24 Years of Space Weather ScienceAfter 24 years mapping Earth’s magnetosphere, ESA’s Cluster mission concluded with a precisely controlled reentry over the South Pacific. This analysis explores the scientific legacy, engineering decisions, and debris mitigation principles behind one of space exploration’s most responsible retirements.
- Mobile Learning and VR in English: What Global Evidence Reveals About Effective Language TechnologyA systematic review across 14 countries reveals which language-learning technologies genuinely work. Mobile learning, AI, and VR show measurable benefits when pedagogically integrated. This evidence-based guide helps educators and learners select technology that delivers real return on investment.
- How AI Agents Will Change the Way We Manage Personal FinancesExplore how AI agents are transforming personal finance through automated budgeting, bill payment, and investment management, while examining the critical security protocols and governance frameworks required for safe deployment.
- CISA’s Ten-Advisory Wave: Why Generic Patching Fails in OT and How to Build Product-Specific PlaybooksCISA released ten ICS advisories in one week, exposing critical infrastructure risks. Generic patching fails in OT. Learn to build product-specific remediation playbooks.
- University Language Proficiency Exams: Why Institutional Tests Demand Different Preparation Than IELTS and TOEFLDiscover why university-specific language proficiency examinations differ fundamentally from IELTS and TOEFL, and learn strategic preparation approaches for institutional assessment success.
- Forbidden Matrix Patterns and Visible Lattice Points: A Geometric DictionaryExplore how multidimensional 0–1 matrices encode geometric truths, linking forbidden patterns to visible lattice points and hypergraph theory, with applications in combinatorics and computational geometry.
RESOURCES
- North Korea denies links to Binance hack as stolen billions are tracedcnbc.com18 hours ago ... North Korea denied allegations linking it to the $6.3 billion Binance hack, calling it a "grave political provocation." Hackers moved…
- North Korea denies involvement in Binance hack, criticizes FBI probeabcnews.com11 hours ago ... North Korea has denied its involvement in the recent cryptocurrency heist at Binance, dismissing as “a trite provocation” a U.S. ...
- North Korea denies being behind record $6.3bn Binance hack - BBCbbc.com11 hours ago ... North Korea has denied claims that it was behind the record $6.3bn (£4.7bn) hack of cryptocurrency exchange Binance, calling the…
- North Korea on Tuesday denied its involvement in the recent ...facebook.com11 hours ago ... North Korea on Tuesday denied its involvement in the recent cryptocurrency heist at Binance ... North Korea denies involvement in…
- FBI says North Korean hackers are behind the theft of $6.3B ... - NPRnpr.org1 day ago ... The FBI is attributing the theft of $6.3 billion from the Binance cryptocurrency exchange to North Korean hackers. North Korea…
- BINANCE HACK: North Korea on Tuesday denied its involvement in ...facebook.com18 hours ago ... BINANCE HACK: North Korea on Tuesday denied its involvement in the recent cryptocurrency heist at Binance, dismissing as “a trite ...
- Binance says outflows normalised as North Korea rejects ... - Reutersreuters.com22 hours ago ... SEOUL/SINGAPORE, Nov 3 (Reuters) - Asset outflows from Binance have normalised and the company was in "very strong financial health",…
- North Korea denies role in $6.4 billion Binance hack after FBI points ...coindesk.com10 hours ago ... The high-profile denial follows FBI alerts identifying North Korean-controlled wallet addresses tied to the largest cryptocurrency exploit ...
- North Korea denies being behind record $6.3bn Binance hack - BBCbbc.co.uk19 hours ago ... The country has consistently denied such claims. Kim Yo Jong said "it is the consistent policy stand of the DPRK…
- Eager to Rebut Rogue-Nation Image, North Korea Denies Role in ...wsj.com11 hours ago ... ... Binance last week.View more. North Korea has denied it was behind the record-breaking $6.3 billion hack of cryptocurrency exchange…
- North Korea denies hacking Sony Pictures - The Guardiantheguardian.comDec 4, 2014 ... It is the first time that North Korea, which is known to have a sophisticated cyber-attack unit, has denied being…
- Binance Hack: What is the Industry Saying after North Korea's Denial?itp.net11 hours ago ... ... North Korea's Denial?. Binance Hack, cryptocurrency, investigation, Kim Jong Un, Kim Yo Jong, North Korea. Cybersecurity.
- North Korea Calls FBI's $6B Binance Claim Absurd [2026]shattered.io3 days ago ... That is the honest state of the North Korea Binance hack story on November 3. The accusation and the denial…
- North Korea Says It Wasn't Behind the $6.3 Billion Binance Hackbusinessinsider.com14 hours ago ... North Korea has denied that it was behind the $6.3 billion theft from cryptocurrency exchange Binance, calling the FBI's allegation…
- North Korea has denied any involvement in the $6.3 billion hack of ...instagram.com18 hours ago ... North Korea has denied any involvement in the $6.3 billion hack of Binance, with senior official Kim Yo-jong calling the…
- 01
- 02
- 03
- 04
- 05
- 06
- 07
- 08
0 Comments