When refrigeration systems across supermarkets in nine European countries failed within a single overnight window, the disruption looked at first like an ordinary technical fault. It was not. Investigators quickly traced the pattern to a suspected cyberattack aimed at the remote-control infrastructure governing frozen-food sections, and the European Union responded by framing the event as a deliberate strike against the bloc's food supply chain. The incident exposed how deeply digital dependency now runs through everyday commerce, where a compromised thermostat can translate directly into spoiled inventory, discarded stock, and shaken consumer confidence.
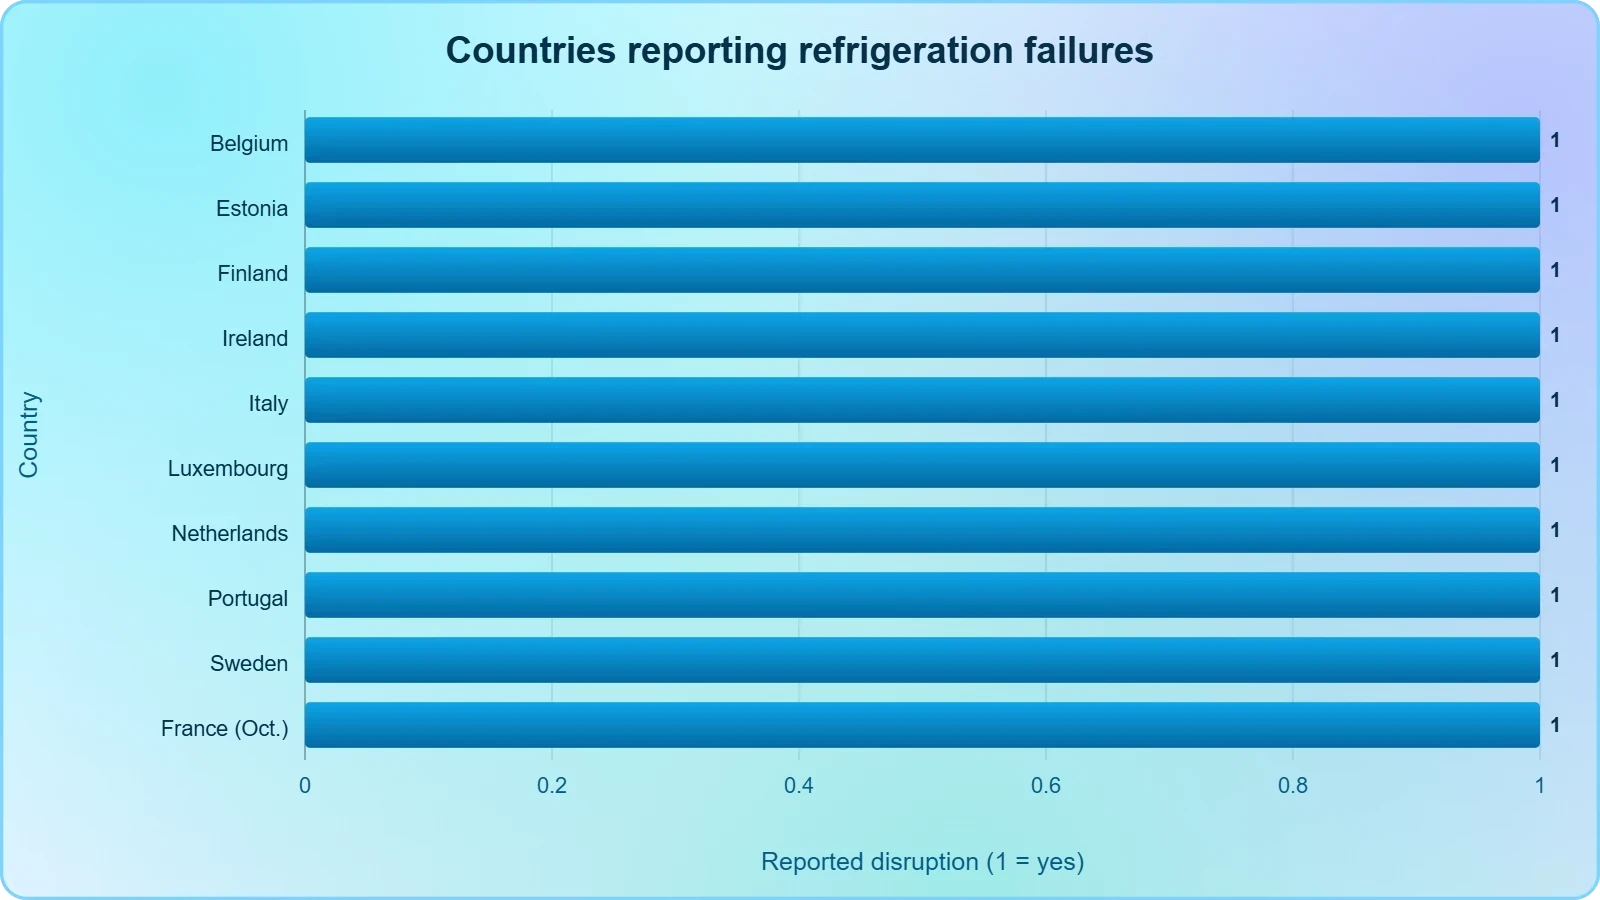
The geography of the disruption is itself revealing. Stores in Belgium, Estonia, Finland, Ireland, Italy, Luxembourg, the Netherlands, Portugal, and Sweden reported failures, while the earlier October attack had already disrupted French grocery outlets and forced hundreds of shops to destroy spoiled food. No group has claimed responsibility for either wave. EU food and agriculture commissioner Christophe Hansen described the incidents as a deliberate attempt to disrupt the food supply chain and undermine public trust in it, a characterization that elevates the matter from routine IT incident to a question of critical infrastructure security and geopolitical pressure.
What makes this case instructive is the supply-chain architecture behind it. Several affected retailers traced their problems to external providers managing refrigeration controls, including Danish manufacturer Danfoss, the same supplier implicated in the October 12 attack on French retailers. Belgian refrigeration firm Sabcobel acknowledged it had begun hardening its installations after the French incident but conceded that some systems had not yet been upgraded when Monday's failures struck. That admission captures the central vulnerability of modern retail: security is only as strong as the slowest vendor to patch, and attackers understand this asymmetry far better than most procurement departments do.
On This Page
TL;DR A suspected cyberattack disabled supermarket refrigeration across nine European countries, forcing retailers to discard food and prompting EU officials to warn of a deliberate effort to destabilize the food supply chain. The incident followed a similar October attack on French grocery stores and appears linked to shared third-party refrigeration-control providers, notably Danfoss. Belgium, Italy, Ireland, Portugal, Sweden, Luxembourg, the Netherlands, Finland, and Estonia all reported disruptions, with national prosecutors and cybersecurity agencies opening investigations. The episode underscores how concentrated vendor dependencies in retail infrastructure create systemic, cross-border exposure that individual retailers cannot resolve alone.
The Anatomy of a Refrigeration Cyberattack
Refrigeration control systems in modern supermarkets are no longer mechanical dials tended by staff. They are networked industrial control environments, often managed remotely by third-party specialists who monitor temperatures, adjust setpoints, and receive alarms across hundreds of sites simultaneously. This centralization delivers efficiency and energy savings, but it also creates a single logical pathway into the cold chain of an entire retail network. When attackers reach that pathway, they do not need to breach every store individually; they inherit the vendor's reach, and the consequences propagate across borders within hours rather than days.
How Remote-Control Systems Became the Target
In Italy, the attack struck at roughly four in the morning and specifically targeted the remote-control system governing frozen-food sections, according to Giuseppe Spadaro, head of the Radenza Group, which manages Coop-branded supermarkets. The timing was not incidental. Overnight windows are when staffing is thinnest and when temperature excursions go unnoticed longest, maximizing the damage before human intervention begins. Spadaro confirmed the issue was subsequently resolved, but the operational lesson endures: the most consequential attacks are often the quietest, exploiting monitoring gaps rather than forcing dramatic system failures that would trigger immediate alarms.
The technical profile of such intrusions typically involves credential compromise, unpatched remote-access services, or exploitation of vendor-side management platforms. Industrial control systems frequently run legacy software with limited authentication hardening, and refrigeration controllers are rarely treated with the same security rigor as payment systems. Attackers who understand this hierarchy can move laterally from a vendor's administrative console into customer environments with modest effort. The result is a class of incident that security researchers have long warned about: low-sophistication access combined with high-consequence physical outcomes, where the digital breach manifests as melted inventory and discarded food rather than stolen data.
Why Food Retail Is Structurally Exposed
Grocery retail operates on extraordinarily thin margins, which historically pushed investment toward inventory turnover and store footprint rather than cyber resilience. Refrigeration represents one of the largest energy costs in any supermarket, making remote optimization economically irresistible and, consequently, making centralized control ubiquitous. The same logic that justifies outsourcing temperature management to a specialist vendor also concentrates risk in that vendor. When Sabcobel admitted that some installations had not yet been upgraded after the October warning, it illustrated a familiar pattern: remediation timelines in operational technology routinely stretch across budget cycles, leaving known gaps open long after the threat is understood.
Consumer trust compounds the exposure. Food safety regulation depends on maintaining cold-chain integrity, and retailers that discard stock face not only direct financial loss but also reputational scrutiny. Commissioner Hansen's framing of the incidents as an effort to undermine consumer confidence recognizes precisely this leverage. An attacker seeking to impose costs on a society does not need to poison anything; disrupting the perception of reliability in daily food access is sufficient to generate political and economic pressure, and supermarkets become unwilling instruments of that strategy.
Belgium and the Prosecutorial Response
Belgium emerged as one of the hardest-hit jurisdictions, with dozens of stores across several grocery chains reporting refrigeration failures and federal prosecutors opening a formal investigation. A Carrefour Belgium spokesman estimated that roughly fifteen of its seven hundred stores were disrupted and attributed the problem directly to a cyberattack. Ikea confirmed that its Mons outlet experienced an intrusion that caused freezer temperatures to rise. Delhaize, Colruyt, and Intermarche also reported problems, while four Delhaize outlets in neighboring Luxembourg were affected, illustrating how a single vendor relationship can spill across national boundaries without regard for regulatory jurisdiction.
From Retail Incident to Criminal Inquiry
The decision by Belgian federal prosecutors to open an investigation signals that authorities are treating the event as potential criminal conduct rather than operational mishap. That shift matters because it unlocks investigative powers, cross-border mutual legal assistance, and the possibility of attribution that commercial incident response cannot achieve alone. Prosecutors will likely examine logs from refrigeration vendors, authentication records, and network telemetry to determine whether the intrusion originated from a state-aligned actor, a criminal group, or an insider. Attribution in operational technology cases is notoriously slow, and the absence of any claim of responsibility complicates the picture further.
Italy moved in parallel, with the national cybersecurity agency confirming affected Coop locations and the government planning a cybersecurity meeting with intelligence services. The involvement of intelligence apparatus reflects a broader European recognition that attacks on food logistics sit at the intersection of economic security and national security. When multiple member states activate prosecutors and spy agencies simultaneously, the political signal is unambiguous: incidents once dismissed as nuisance-level IT problems are now being catalogued as strategic threats requiring coordinated state response.
The Vendor Concentration Problem
Swedish retailer Coop confirmed that six of its roughly eight hundred stores were hit, and a spokesman offered a detail of unusual technical candor: the affected stores had been connected to a 4G mobile network rather than the newer 5G system, which made them more exposed to hackers. Swedish chain Ica reported limited refrigeration problems without confirming an attack, noting that affected stores were connected to an external control system provided by Danfoss, the same supplier targeted in the October 12 cyberattack on French retailers. Danfoss did not respond to requests for comment, leaving open the question of how far the vendor-side compromise extended.
This concentration is the structural heart of the story. When a single refrigeration-control supplier serves retailers across multiple countries, a compromise of that supplier becomes a systemic event rather than a localized one. Regulators have spent years addressing concentration risk in banking and cloud computing, yet the operational technology layer of food retail has received comparatively little scrutiny. The nine-country footprint of this incident suggests that vendor concentration in industrial control systems deserves the same supervisory attention that financial regulators already apply to critical service providers, because the failure mode is identical in principle even if the sector differs.
The EU's Political Framing and Food Security
Commissioner Christophe Hansen's characterization of the incidents as a deliberate attempt to disrupt the food supply chain and undermine consumer confidence represents a significant rhetorical escalation. Brussels rarely applies the language of deliberate disruption to commercial IT failures, and doing so here signals that the Commission views the events through a security lens rather than a consumer-protection one. The framing also creates political obligations: once an event is labeled an attack on the food supply chain, member states face pressure to demonstrate coordinated response, information sharing, and hardened standards across a sector that has historically been regulated for hygiene rather than cyber resilience.
Why Consumer Confidence Is the Real Target
Food supply chains depend on predictability. Shoppers assume that frozen goods remain frozen, that cold storage is reliable, and that the infrastructure behind a supermarket aisle is boring and dependable. An attack that makes freezer temperatures rise overnight attacks that assumption directly, and the psychological effect extends well beyond the stores involved. Even consumers in unaffected countries read about discarded stock and begin to question the resilience of the system they rely on daily. Undermining confidence is cheaper than causing scarcity, and it produces political friction without requiring the attacker to sustain a prolonged campaign.
The economic damage is also asymmetric in the attacker's favor. Discarded food represents a direct loss to retailers, but the larger cost lies in remediation, vendor audits, system upgrades, and the operational distraction of responding to prosecutors and regulators. For a modest investment in exploiting an unpatched remote-access service, an adversary can impose costs measured in millions across multiple jurisdictions. This asymmetry explains why critical infrastructure attacks persist despite years of warnings: the economics favor the attacker, and the defender must protect every entry point while the intruder needs only one.
Regulatory Gaps in Operational Technology
European regulation has advanced considerably on data protection and network security, yet operational technology in retail sits in an awkward gap. The NIS2 directive expands obligations to food distribution, but implementation varies by member state, and enforcement against third-party vendors remains uneven. Refrigeration controllers rarely fall under the same scrutiny as payment terminals, even though their failure produces immediate physical consequences. The nine-country incident suggests that supervisory attention should follow the vendor relationship rather than the retail brand, because the brand is often the last party to learn that its cold chain has been compromised.
There is also a transparency deficit. Several retailers confirmed problems without confirming an attack, and the primary supplier declined to comment. This reticence is understandable commercially but problematic for collective defense, since other customers of the same vendor cannot assess their own exposure without disclosure. Security researchers have long argued that incident reporting in operational technology should be mandatory and timely, precisely because the harm is systemic. The current pattern, where facts emerge through media reports and national agencies rather than coordinated disclosure, slows the response that shared infrastructure demands.
We Also Published
- 01
- 02
- 03
- 04
Technical Lessons for Industrial Control Security
The incident offers a compact case study in the failure modes of industrial control security. Remote-control systems for frozen-food sections are, functionally, supervisory control and data acquisition environments operating at modest scale. They prioritize availability and ease of maintenance over adversarial hardening, and they are frequently administered by third parties whose credentials grant broad reach. When attackers obtain those credentials, they inherit legitimate access rather than needing to exploit a novel vulnerability. The resulting intrusion can look, from the retailer's perspective, indistinguishable from a vendor maintenance action until temperatures begin to climb.
Network Choice and Attack Surface
The Swedish detail about 4G versus 5G connectivity deserves closer attention than it received. Coop's spokesman indicated that affected stores were connected to a 4G mobile network rather than the newer 5G system, which made them more exposed to hackers. The precise mechanism is debatable, but the underlying principle is sound: connectivity choices determine attack surface, and legacy cellular links may lack the isolation and monitoring that newer deployments provide. Retailers rarely treat network generation as a security decision, yet the incident suggests that connectivity architecture belongs in the same risk register as patching and access control.
More broadly, the episode reinforces the case for network segmentation between corporate IT and operational technology. Refrigeration controllers should not share routable paths with point-of-sale systems, and vendor remote access should be brokered through monitored jump hosts with session recording. None of these controls is novel; all are routinely recommended. Their absence in production environments reflects budget priorities rather than technical ignorance. The nine-country disruption is the cost of that gap, and it will likely accelerate adoption of zero-trust principles in retail operational technology, however unevenly.
Incident Response Across Borders
Coordinated response across nine jurisdictions is inherently difficult. Each country has its own cybersecurity agency, legal framework, and disclosure norms, and retailers operate under commercial confidentiality that discourages candor. The Italian government's decision to convene intelligence services and Belgium's prosecutorial investigation illustrate two different institutional reflexes responding to the same event. Harmonizing those reflexes is precisely what EU-level coordination is meant to achieve, yet the incident shows how much still depends on national initiative. A shared vendor, a shared vulnerability, and a shared timeline ought to produce a shared response, but institutional fragmentation slows what technology enables.
For retailers, the practical lesson is that incident response plans must extend beyond their own perimeter. When the failure originates at a vendor, the retailer's plan must include vendor escalation paths, contractual obligations for notification, and contingency procedures for manual temperature management. Sabcobel's partial remediation after the October warning suggests that contractual pressure to upgrade was insufficient. Future procurement will likely embed security baselines and remediation deadlines into refrigeration contracts, converting a technical recommendation into a commercial obligation with financial consequences for non-compliance.
Implications for Retailers, Insurers, and Regulators
The commercial consequences of this incident will unfold over quarters rather than days. Retailers face direct losses from discarded stock, but the more significant costs lie in remediation programs, vendor renegotiations, and the insurance implications of a newly demonstrated risk class. Insurers covering business interruption have historically modeled refrigeration failure as equipment breakdown, a relatively predictable peril. A cyber-induced refrigeration failure sits awkwardly between cyber and property policies, and the nine-country scope will likely prompt underwriters to revisit exclusions, sublimits, and the evidence required to prove that a temperature excursion resulted from malicious action rather than mechanical fault.
Insurance and Liability Questions
Liability allocation will be contested. Retailers will look to refrigeration vendors, vendors will point to contractual limitations, and insurers will examine whether policyholders maintained reasonable security controls. The Sabcobel admission that some systems had not yet been upgraded creates a documentary trail that claimants and insurers will scrutinize closely. In European jurisdictions, the question of whether a vendor's delayed remediation constitutes negligence is fact-specific, but the existence of a prior warning three weeks earlier materially strengthens arguments that the risk was known and mitigable. Expect contractual indemnities in refrigeration agreements to receive far more legal attention in the coming procurement cycles.
For smaller retailers, the exposure is proportionally larger. A corner shop in the Netherlands or a small Kesko-affiliated store in Finland lacks the legal resources to pursue a multinational vendor and the technical staff to audit control systems. This asymmetry means that the burden of resilience falls hardest on those least equipped to bear it, a familiar pattern in supply-chain security. Industry associations and national agencies may need to provide shared assessment tools so that small operators can evaluate vendor security without building in-house capability that their margins cannot support.
What Comes Next for EU Policy
Brussels has been moving toward treating food distribution as critical infrastructure, and this incident provides the political momentum to accelerate that shift. Expect renewed emphasis on supply-chain security requirements, mandatory incident reporting timelines, and supervisory scrutiny of third-party technology providers. The Commission's language about deliberate disruption also opens the door to attributing such attacks under the EU's cyber diplomacy toolbox, which permits sanctions against responsible actors. Attribution remains uncertain, but the policy machinery is now primed to respond if evidence emerges, and that readiness itself functions as a deterrent signal.
Retailers, meanwhile, should treat the incident as a prompt to inventory their operational technology dependencies with the same rigor applied to financial systems. Mapping which vendors can reach which controllers, verifying patch status, enforcing multi-factor authentication on remote access, and rehearsing manual fallback procedures are unglamorous measures that would have limited this disruption. The lesson of the nine-country outage is not that refrigeration is uniquely fragile, but that concentrated digital control of physical processes creates systemic risk which individual actors cannot manage alone. Collective defense requires collective visibility, and visibility begins with disclosure.
Reading the Incident in a Wider Strategic Context
Attacks on food logistics belong to a broader pattern in which adversaries target the mundane infrastructure of daily life rather than symbolic or governmental targets. Ports, pipelines, logistics platforms, and now supermarket refrigeration all share a characteristic: they are essential, privately operated, and unevenly defended. The strategic logic is to generate friction and doubt at scale while remaining below the threshold of armed conflict. Because no group has claimed responsibility, the incident also demonstrates how ambiguity itself serves an attacker's purposes, complicating attribution and delaying the political response that clarity would enable.
Attribution and the Problem of Silence
The absence of any claim of responsibility is notable but not unusual. State-aligned actors rarely advertise operations against civilian infrastructure, and criminal groups typically prefer to monetize access rather than publicize it. In this case, the intrusion pattern, the targeting of a specific vendor, and the timing relative to the French incident suggest deliberate coordination, but suggestion is not proof. Investigators will need forensic evidence from vendor systems, and the vendor's silence complicates that effort. Until attribution is established, the EU's cyber diplomacy tools remain available but unusable, which is precisely the limbo that sophisticated attackers seek to occupy.
Silence also shapes deterrence. If an adversary can impose costs without being named, the deterrent effect of potential sanctions is diminished, and the incentive to repeat the operation remains intact. This is why the Commission's public characterization matters: naming the conduct as deliberate disruption builds a political record that can support future attribution and response. It also signals to member states that the incident is not a private commercial matter to be resolved between retailers and vendors, but a collective security concern requiring shared intelligence and coordinated messaging.
Preparedness as the Only Reliable Defense
Given the difficulty of attribution and the speed of propagation across borders, preparedness remains the most reliable defense. Retailers that maintained manual fallback procedures, monitored temperatures continuously, and segmented vendor access suffered less than those that did not. The Swedish decision to reconnect affected stores to a different network illustrates practical improvisation under pressure, but improvisation is not a strategy. Durable resilience requires designing refrigeration control with the assumption that remote access will eventually be compromised, and building detection and containment around that assumption rather than treating it as a remote possibility.
The wider lesson extends beyond groceries. Any sector that has centralized control of physical processes into a small number of vendors inherits the same structural vulnerability, whether the process involves cold storage, water treatment, or building management. The nine-country refrigeration outage is a preview of how such vulnerabilities manifest at scale: quietly, overnight, across jurisdictions, and with consequences that are measured in discarded food and diminished trust. The response must be equally systemic, combining vendor accountability, regulatory oversight, and the unglamorous discipline of maintaining and testing the controls that already exist.
From our network :
- Committed Mediterranean Precipitation Decline: Why Emissions Cuts Alone Cannot Restore Winter RainsNew NOAA research reveals that Mediterranean winter rains may decline irreversibly even with emissions cuts. Explore the science of committed climate change and regional impacts.
- The Hidden Cost of AI Convenience: Why Over-Permissioned Agents Are a Security Time BombDiscover why AI agents with excessive permissions create dangerous single points of failure, and learn how implementing least privilege principles can protect your organization from exploitation.
- Live Online English Classes for Kids: Do They Actually Reduce Anxiety?A ten-week study reveals that synchronous online English classes can significantly reduce child language anxiety while improving listening and reading skills. Discover what makes these programs effective and how parents can select the right one.
- Mobile Learning and VR in English: What Global Evidence Reveals About Effective Language TechnologyA systematic review across 14 countries reveals which language-learning technologies genuinely work. Mobile learning, AI, and VR show measurable benefits when pedagogically integrated. This evidence-based guide helps educators and learners select technology that delivers real return on investment.
- How AI Agents Will Change the Way We Manage Personal FinancesExplore how AI agents are transforming personal finance through automated budgeting, bill payment, and investment management, while examining the critical security protocols and governance frameworks required for safe deployment.
- University Language Proficiency Exams: Why Institutional Tests Demand Different Preparation Than IELTS and TOEFLDiscover why university-specific language proficiency examinations differ fundamentally from IELTS and TOEFL, and learn strategic preparation approaches for institutional assessment success.
- Forbidden Matrix Patterns and Visible Lattice Points: A Geometric DictionaryExplore how multidimensional 0–1 matrices encode geometric truths, linking forbidden patterns to visible lattice points and hypergraph theory, with applications in combinatorics and computational geometry.
- CISA’s Ten-Advisory Wave: Why Generic Patching Fails in OT and How to Build Product-Specific PlaybooksCISA released ten ICS advisories in one week, exposing critical infrastructure risks. Generic patching fails in OT. Learn to build product-specific remediation playbooks.
- The Final Descent: How ESA Retired the Legendary Cluster Constellation After 24 Years of Space Weather ScienceAfter 24 years mapping Earth’s magnetosphere, ESA’s Cluster mission concluded with a precisely controlled reentry over the South Pacific. This analysis explores the scientific legacy, engineering decisions, and debris mitigation principles behind one of space exploration’s most responsible retirements.
RESOURCES
- New cyberattack on supermarket fridges sweeps across Europereuters.com2 days ago ... STOCKHOLM/BRUSSELS/LONDON, Nov 2 (Reuters) - A hacking attack on European supermarkets spread across the continent on Monday, hitting fridges ...
- Here's what to know about another cyberattack on European ... - PBSpbs.org9 hours ago ... It's a repeat of an earlier incident that struck refrigeration systems in hundreds of supermarkets and independent stores across France,…
- Supermarkets across Europe hit by new fridge cyberattacksnbcnews.com2 days ago ... Supermarkets across Europe hit by new fridge cyberattacks ... The incidents caused temperature spikes and spoiled food at stores in…
- Shop freezers in seven European countries hit by cyber-attack - BBCbbc.com2 days ago ... Dozens of supermarkets across seven European countries have been hit by a cyber-attack affecting their refrigerators and freezers.
- Cyberattacks disrupt refrigeration systems at European supermarketspbs.orgOct 13, 2026 ... French Finance Minister Roland Lescure told Parliament on Tuesday that about 700 of the country's 10000 supermarkets were affected.
- Suspected cyberattacks trigger supermarket fridge failures across ...aljazeera.com2 days ago ... Suspected cyberattacks have triggered temperatures to rise in grocery store refrigeration systems in a growing number of countries across Europe ...
- Shop fridges and freezers across Europe hit by fresh suspected ...theguardian.com2 days ago ... Supermarket chains in at least seven European countries have said the temperatures of refrigerators and freezers in some of their…
- More grocery stores in Europe report fridge and freezer temperature ...cbsnews.com2 days ago ... 12, major French retailers said hundreds of stores were hit by a cyberattack on their refrigeration systems, which forced them…
- New Wave Of Refrigerator Cyberattacks Roils European Supermarketsforbes.com2 days ago ... Topline. Supermarkets across Europe were again targeted in cyberattacks Monday, which heated refrigerators to temperatures above 120 degrees ...
- Cyberattack hits 700 supermarkets in France, sparking investigationapnews.comOct 13, 2026 ... PARIS (AP) — Cyberattacks disrupted European supermarket chains, affecting refrigeration systems at hundreds of stores in France and forcing ...
- Fridge cyberattack hits supermarkets across Europe - AFP.comafp.com2 days ago ... A suspected cyberattack hit grocery stores across at least nine European countries on Monday, prompting the EU to warn of…
- Second wave of refrigeration cyberattacks hits European supermarketshelpnetsecurity.com2 days ago ... Three weeks after the rattack on freezers in French supermarkets, similar cyberattacks have hit shops in other European countries.
- Supermarket freezers across Europe hit by suspected cyberattackapnews.com1 day ago ... Cyberattacks disrupted refrigeration and freezer systems at supermarkets across Sweden on Monday, forcing some stores to discard spoiled ...
- Supermarket fridges hit with cyberattacks across Europe - CNBCcnbc.com20 hours ago ... Empty refrigerated shelves following a refrigeration outage at a Proxy Delhaize store in Maleizen, Overijse, Belgium, on Monday, Nov. 2,…
- Cyberattack Hits Hundreds of Supermarket Refrigeration Systems in ...nytimes.comOct 13, 2026 ... The attack targeted a Danish software system in more than 400 supermarkets, forcing some shops to throw out frozen produce.…
- 01
- 02
- 03
- 04
- 05
- 06
- 07
- 08
0 Comments